The Two Classes of Vulnerability
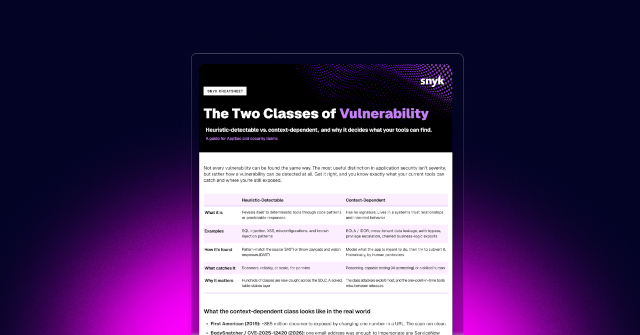
Not every vulnerability can be found the same way. The most useful distinction in application security isn't severity, but rather how a vulnerability can be detected at all. Get it right, and you know exactly what your current tools can catch and where you're still exposed. Vulnerabilities typically appear in two classes: heuristic-detectable and context-dependent. Heuristic-detectable reveals itself to deterministic tools through code patterns of predictable responses, while context-dependent has no signature, living in a system’s trust relationships and intended behavior. Download this cheatsheet to discover how to offset these vulnerabilities, and what it means for your security program.
Report Snapshot
Why heuristic-detectable flaws like SQLi, XSS, and misconfigurations are a solved, table-stakes layer
Why context-dependent flaws like BOLA/IDOR and auth bypass are the class that attackers exploit most
What kind of testing it takes to catch the flaws scanners structurally can’t